CAPABILITIES · OPSGATE

Everything between the keystroke and the leak.

OpsGate decides at the moment of sending: what is sensitive, how risky it is, what to do about it, and what to record. Six capabilities, one boundary.

Signature

Secure Rewrite

Sensitive fragments are rewritten in place, with a side-by-side preview and a risk score before and after. The model still receives a usable prompt, and the secret never travels.

  • Original against secured text, side by side
  • The same request scored before and after the rewrite
  • Code blocks, tables and line breaks preserved
Risk score and simulation

Every prompt gets an explicit 0 to 100 score with the factors behind it. From 40 upward, a simulation lists exactly what would leak before anything is sent.

  • Score built from rule severity, volume and context
  • The simulation names the fragments, not a verdict
  • Policy can act at 40, 60 or 90

Shadow AI discovery

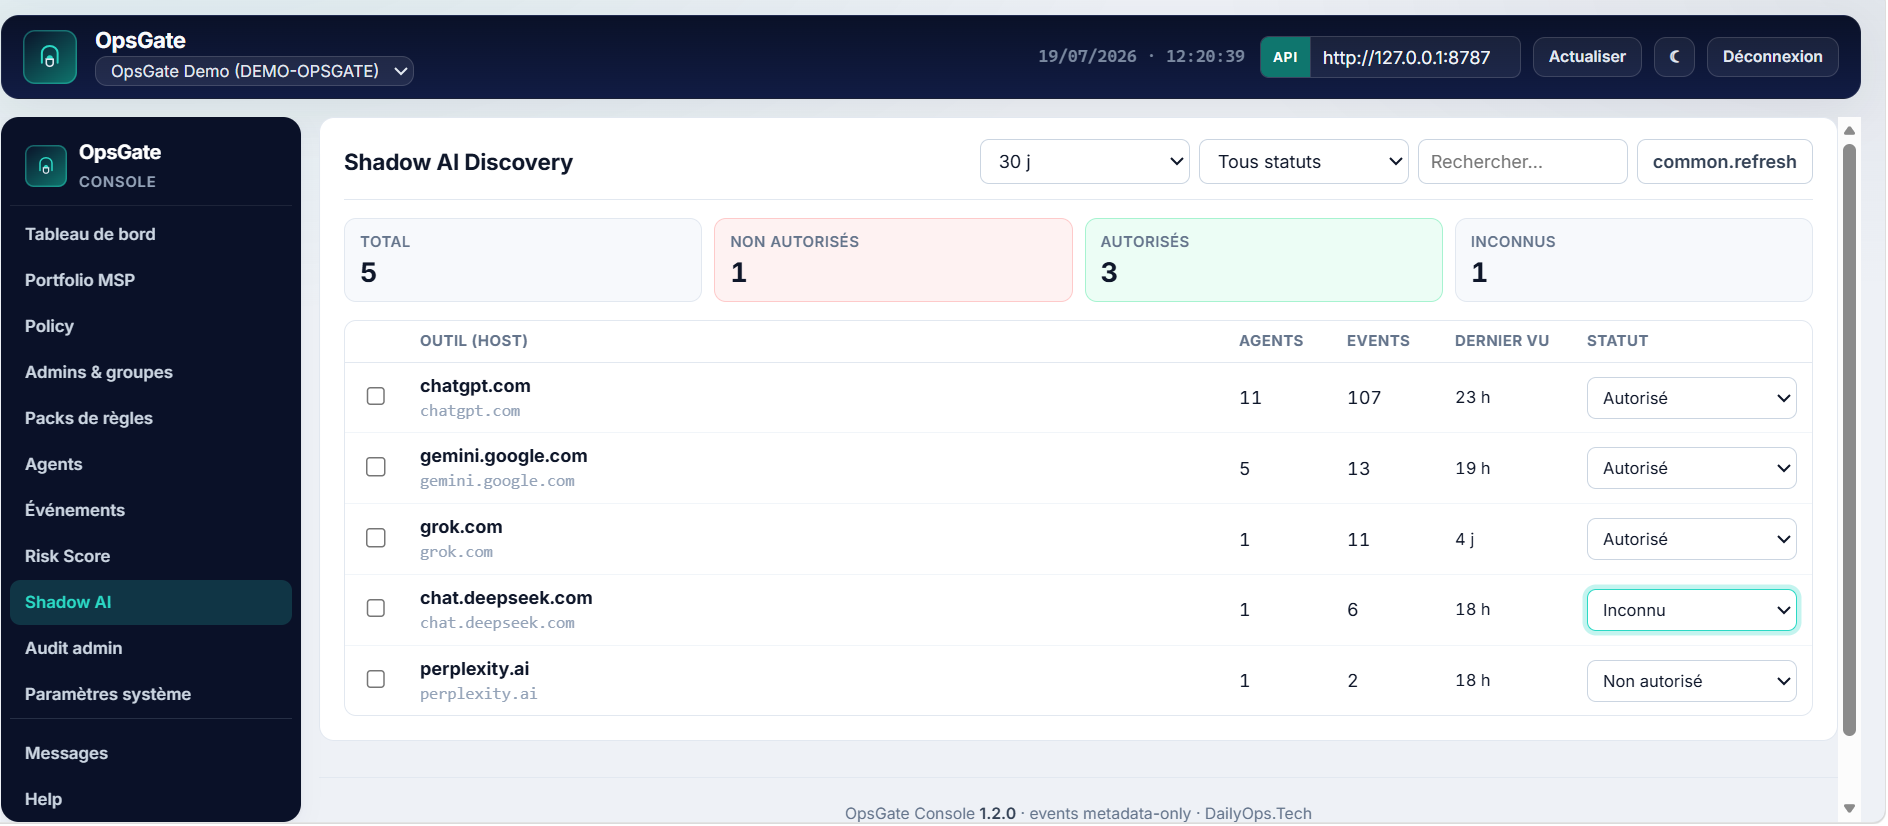
See which AI tools your teams actually use, authorized or not, with the number of agents and events per host. The policy conversation starts from facts instead of assumptions.

  • Per-host status: authorized, unknown, unauthorized
  • Agents and events per host over 30 days
  • Host lists configurable per tenant
OpsGate console: Shadow AI Discovery, cinq hôtes IA détectés avec leur statut d'autorisation.
Console · Shadow AI Discovery

Files and OCR, scanned locally

PDF, DOCX, PPTX, XLSX, code, SQL, database files and screenshots pass through quarantine. OCR reads images on the device, and masked versions are reinjected with the format preserved.

  • Quarantine before the upload leaves the browser
  • OCR runs on the workstation, not on a server
  • Masked file returned in its original format

One console, every decision

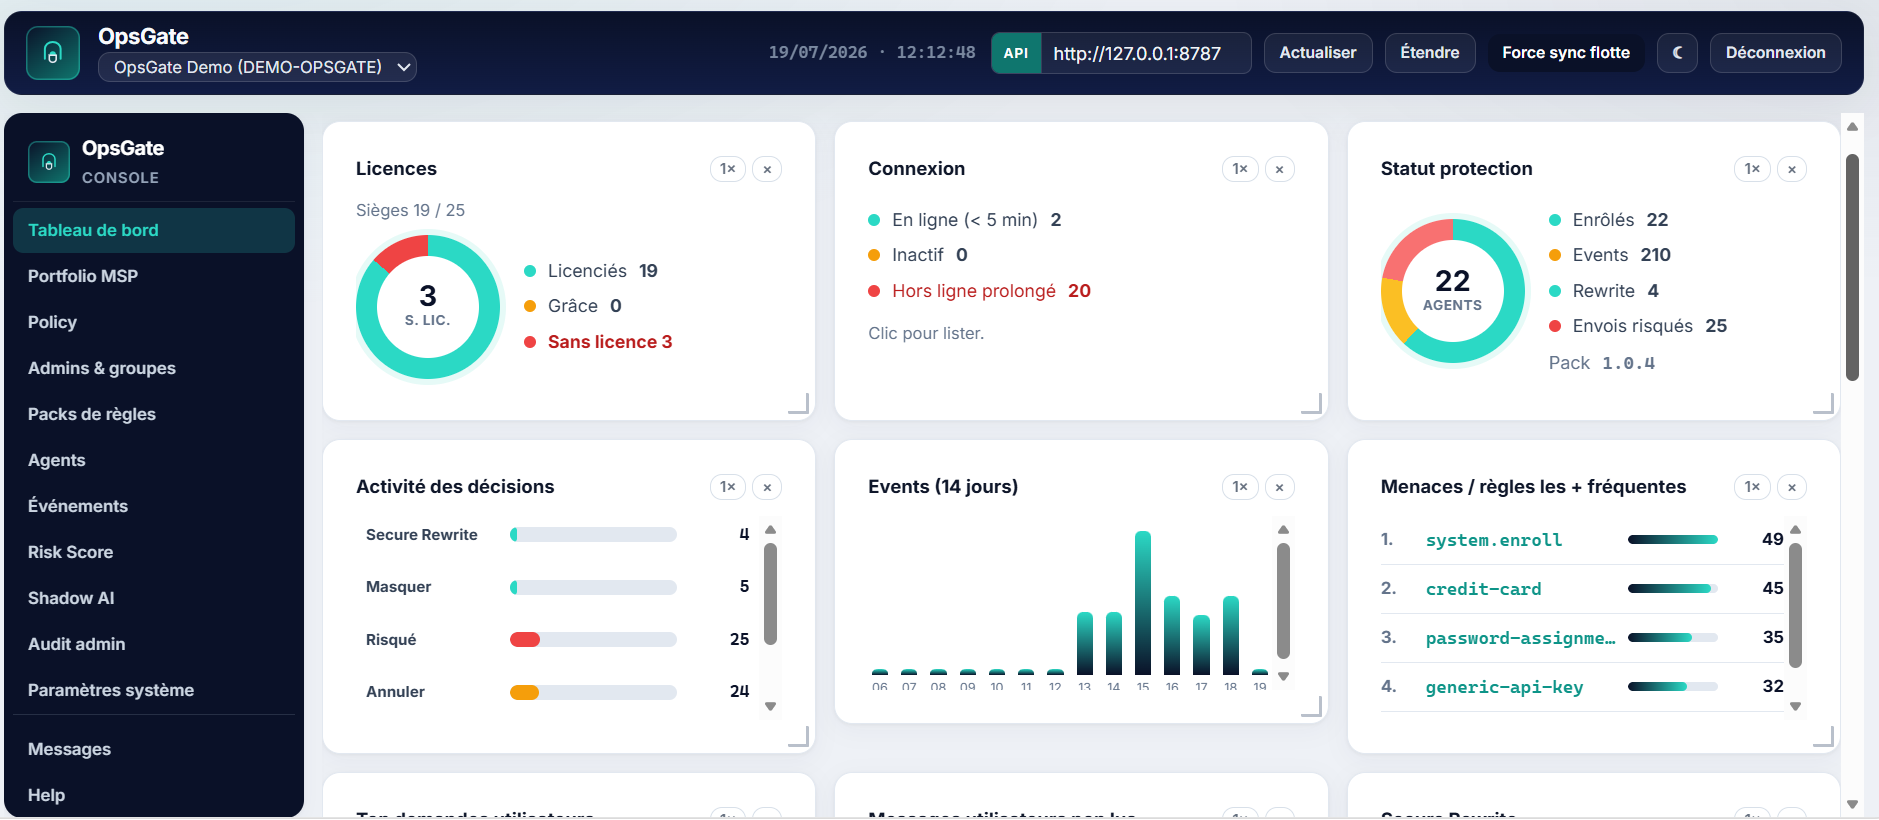
Decisions, risks, shadow AI, policy and audit live on the same control plane. Licences, protection status and the decision breakdown are visible at a glance.

  • Decision activity: rewrite, mask, risky, cancel
  • Events over 14 days and top rules fired
  • Per-tenant isolation with row-level security
OpsGate console: licences, connexion, statut de protection, activité des décisions et événements sur 14 jours.
Console · tableau de bord

Signed rule packs, hot updates

Detection rules ship as ed25519-signed packs, versioned and updated without rebuilding or redeploying. The engine explains its detections, it is not a black box.

  • Versioned packs with an explicit changelog
  • Signature verified before a pack is applied
  • Detection tuned for infrastructure configs and cloud keys

WHY IT IS DIFFERENT

Enable AI. Secure data.

Most DLP tools treat AI as a threat to shut down. OpsGate treats it as a boundary to operate: explicit, explainable and evidence-ready.

A filet, not a wall

OpsGate does not block sites and does not spy on your teams. It scans at the instant of sending, recommends the safe path, and leaves the final decision visible.

  • Detection at send time only, no keylogging
  • Banner in an isolated shadow DOM, immune to site styles
  • Observe or enforce modes, per tenant policy

Defense in depth

The extension covers the DOM. The optional MITM proxy covers the network with the same detection engine, one single source of truth for what is sensitive.

  • Shared engine across extension, proxy and console
  • HTTP/2 MITM with deep multipart scanning
  • Windows MSI with portable Node, deployable by GPO or MDM

Evidence for the audit

When an auditor asks what left and why, the answer is a query, not an investigation.

  • Write-once (WORM) audit trail, SHA-256 chained
  • SIEM export: syslog, CEF, OTel
  • Prometheus metrics endpoint and GDPR soft-delete

GOVERNANCE

The control plane behind the boundary.

OpsGate is multi-tenant by design, with row-level security in PostgreSQL, ready for MSPs managing several client organizations.

SSO OIDC / SAMLMFA TOTPPasskeys WebAuthnWORM auditSIEM / PrometheusGDPR soft-deleteRLS multi-tenantMSP portfolio

Identity done properly

SSO with OIDC (Entra, Okta) and SAML 2.0 fail-closed, MFA including TOTP and passkeys with Windows Hello, and a session challenge on concurrent logins.

Policies people can read

Default policy plus departmental profiles, rule packs assignable by group, and console messages your teams actually see when a prompt is handled.

Honest retention

Events keep metadata only, with 90-day minimum retention, scheduled exports, a security report in PDF, and a documented GDPR soft-delete path.

Put a defensible boundary around enterprise AI use.

Run a pilot with your own teams and your own AI tools this week. We onboard early access organizations personally.

Request early access Read the repository Early access pilots include deployment support from DailyOps.

Need a hand? I can help with guides and tech topics.